7 Best Open Source Zerotier Alternatives
A curated collection of the 7 best open source and self-hosted alternatives to Zerotier in 2026.
Looking for a free, privacy-friendly, or self-hosted replacement for Zerotier in 2026? The top open-source alternative is Tailscale — Zero-config VPN for secure remote access.
Other highly rated open-source Zerotier alternatives include Netbird, Pangolin and FireZone.

Zero-config VPN for secure remote access
Tailscale is a modern VPN solution that simplifies secure remote access using the power of WireGuard. Built on top of WireGuard, it adds zero-configuration setup, built-in two-factor authentication (2FA), and end-to-end encryption to create a seamless and secure networking experience. - Zero-Config VPN: No complex firewall rules or port forwarding required. Tailscale works out of the box with minimal setup. - Built-in 2FA: Adds an extra layer of security with two-factor authentication for all users. - End-to-End Encryption: All traffic is encrypted using WireGuard’s state-of-the-art encryption protocols. - Cross-Platform Support: Works on Windows, macOS, Linux, iOS, Android, and more. - Device Discovery: Automatically discovers and connects devices on your network. - ACL & Access Control: Fine-grained access control with Tailnet policies to manage who can access what. - MagicDNS: Automatically assigns human-readable DNS names to devices (e.g., mydevice.tailnet-name.ts.net). - Relay & DERP Servers: Built-in relay servers ensure connectivity even behind restrictive firewalls. - Open Source: The core components are open-source, allowing for transparency and community contributions. - Enterprise Ready: Scalable solution for teams and organizations with centralized management and monitoring. Tailscale is primarily a managed service, but it is built on open-source components and can be self-hosted for advanced users. The control plane (coordination server) is managed by Tailscale, Inc., but the client and relay servers are open-source. Users can deploy their own DERP (Distributed Encryption Relay Protocol) servers for enhanced privacy and control. Tailscale supports various deployment models, including cloud, on-premises, and hybrid setups.

Open source Zero Trust Networking platform
NetBird is a WireGuard®-based overlay network and Zero Trust Network Access (ZTNA) platform designed to securely connect remote users, hybrid-cloud, and edge infrastructure. It replaces legacy VPNs with an identity-based access control system, providing secure remote access, zero-config deployment, seamless SSO with MFA, dynamic posture checks, and centralized network management. - Secure Remote Access: Least privilege network access with user and group provisioning from identity providers (Okta, Microsoft, Google, etc.) - Zero-Config Deployment: Peer-to-peer WireGuard®-based network that runs on almost any platform in minutes without firewall configurations or open ports - Seamless SSO with MFA: Session-based single sign-on and multi-factor authentication using existing identity provider settings - Dynamic Posture Checks: Enforce security policies for managed devices, including firewall, antivirus, geo-location, and network location checks - Centralized Network Management: Control private networks from a single dashboard with detailed activity logging and integrations - AI Agent Network: Distribute AI access without sharing LLM API keys, with per-team cost control and full audit trails - Compliance & Security: GDPR, ISO 27001, and DORA compliant with detailed audit logs and security posture checks NetBird offers both a cloud-hosted solution and a self-hosted open-source version. The self-hosted deployment includes: - Open Source Core: Available under the AGPL-3.0 license on GitHub - Self-Hosting Documentation: Comprehensive guides for deploying on various platforms including Docker, Kubernetes, and bare metal - Scalability: Designed for enterprise-grade deployments with support for distributed teams and hybrid-cloud environments - Integrations: Compatible with identity providers (Okta, Microsoft Entra ID, Google Workspace), MDM/EDR solutions, and monitoring tools

Zero trust remote access platform replacing traditional VPNs
Pangolin is an open-source, identity-based remote access platform designed to replace traditional VPNs with a zero-trust architecture. Built for IT/OT, IoT, and engineering teams, Pangolin provides unified, secure access to applications and infrastructure across on-prem, cloud, and edge environments. - Zero Trust Access: Enforce identity and context-aware rules for granular access control - Multi-Protocol Support: Secure access to SSH, web apps, RDP, databases, and APIs - Peer-to-Peer Tunnels: Direct connections via WireGuard® for high performance - Clientless Browser Access: No client installation required for web-based resources - Unified Dashboard: Centralized management and monitoring of all remote access - Identity Integration: Connects with existing identity providers (SSO, OAuth, etc.) - Cross-Platform Support: Native clients for macOS, Windows, Linux, iOS, and Android - Self-Hosted & Cloud: Deploy on-premises or in your preferred cloud environment - AI Gateway: Built-in support for connecting to cloud and self-hosted AI models (v1.22+) Pangolin is built on WireGuard® and released under an open-source license. The platform can be self-hosted on any infrastructure or used via Pangolin's managed cloud service. The connector can be deployed behind any firewall, making it suitable for secure enterprise environments. Documentation and downloads are available at docs.pangolin.net.
Replace your VPN with zero-trust access built on WireGuard. Fast, scalable network security with simple policies and identity provider integration.
Replace your VPN with zero-trust access built on WireGuard. Fast, scalable network security with simple policies and identity provider integration.

Zero-trust access management with WireGuard 2FA
DefGuard is a self-hosted zero-trust access management platform that combines WireGuard VPN with robust 2FA/MFA capabilities. Designed for teams and enterprises, it provides secure remote access without compromising security or privacy. - WireGuard Integration: Native WireGuard VPN support for high-performance secure networking - Multi-Factor Authentication: Built-in 2FA/MFA with TOTP, hardware keys, and backup codes - Zero-Trust Architecture: Enforces least-privilege access controls and continuous verification - Self-Hosted: Full control over data with on-premise or private cloud deployment - User Management: Centralized user provisioning, roles, and permissions - Audit Logging: Comprehensive activity tracking and compliance reporting - Multi-Platform Support: Works with Windows, macOS, Linux, and mobile devices - Open Source: Transparent codebase with community-driven development DefGuard is built with Go and TypeScript, using PostgreSQL for data storage. The platform can be deployed via Docker containers or directly on bare metal servers. Comprehensive documentation is available for Kubernetes deployments and production setups. All components are designed for high availability and scalability.
Secure end-to-end encrypted messenger for organizations
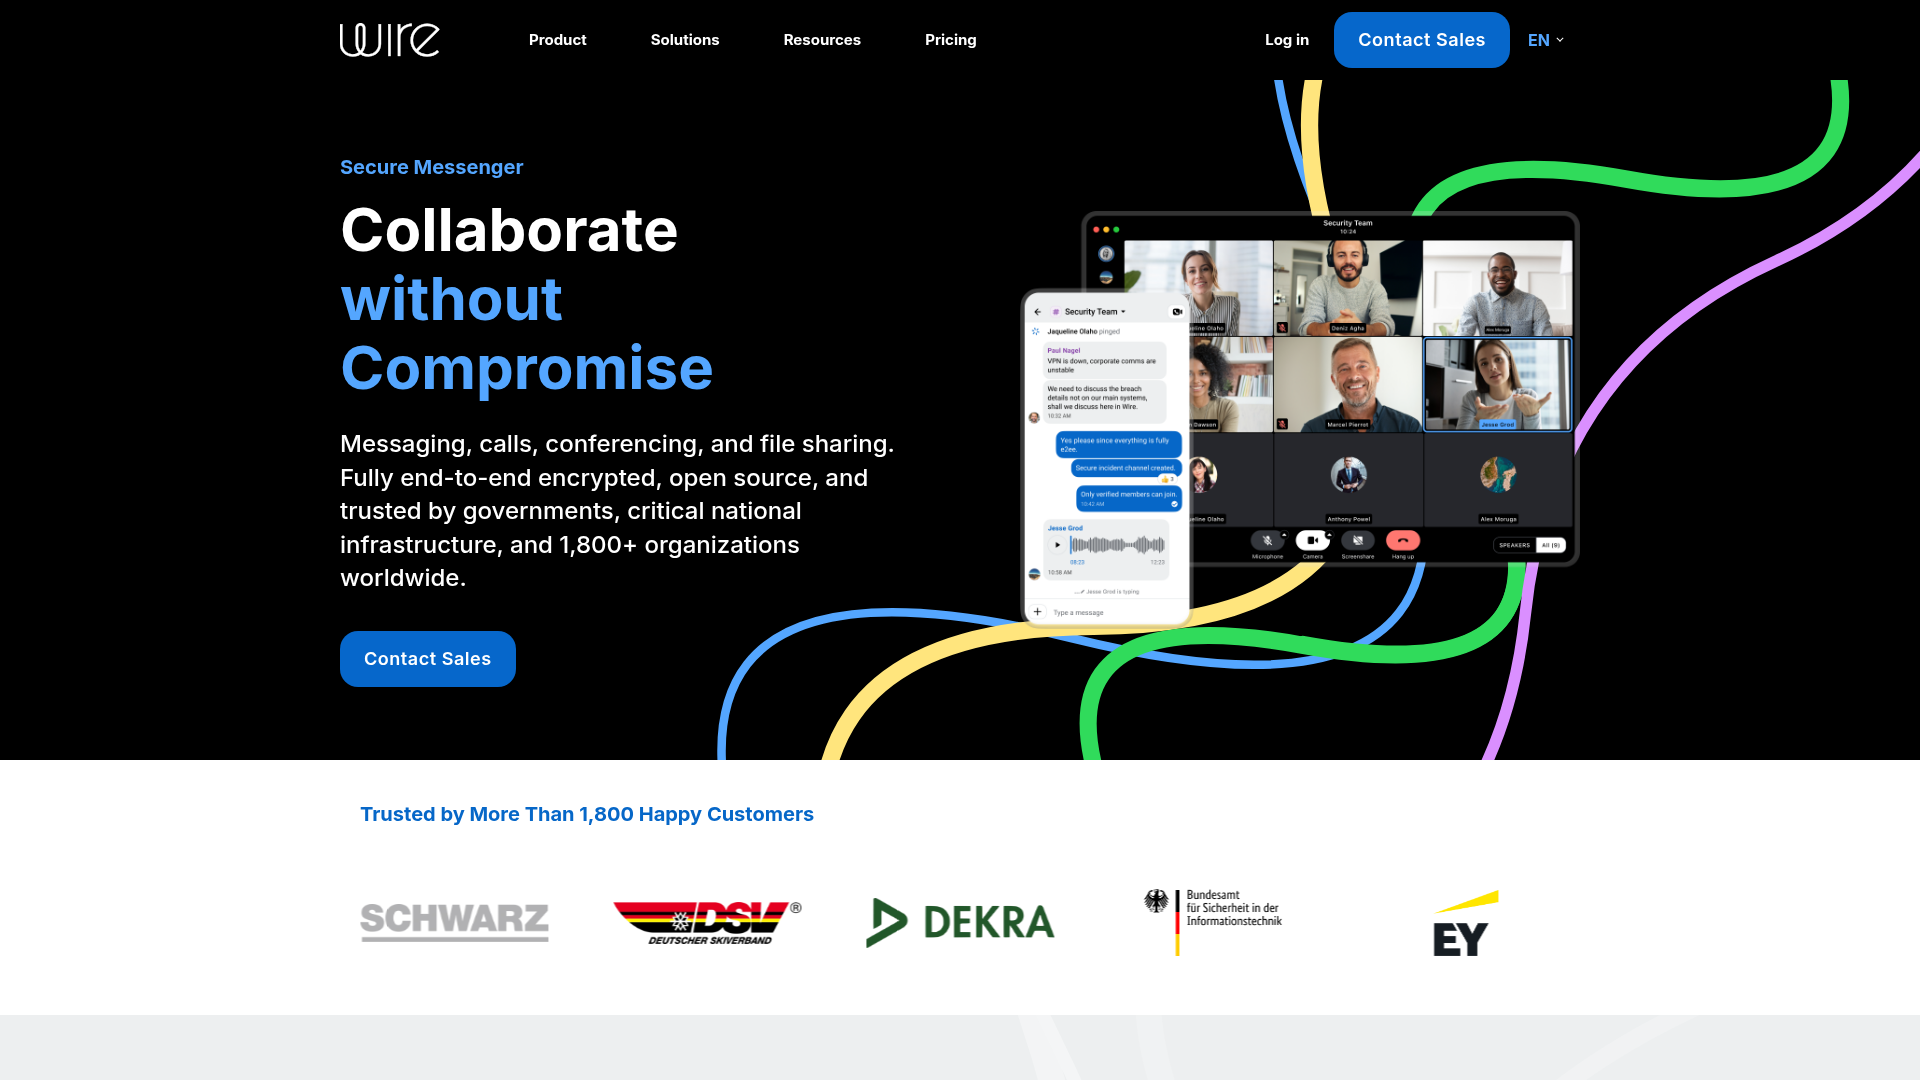
Wire is a trusted secure communication platform designed for organizations worldwide. Built with invisible end-to-end encryption, Wire ensures all conversations and data remain private and protected at all times. - End-to-End Encryption: All messages, calls, and files are encrypted by default, ensuring complete privacy. - Flexible Deployment: Choose from cloud, on-premises, or hybrid deployment to meet organizational needs. - Enterprise-Grade Security: SSO, granular permissions, and compliance-ready security for regulated environments. - Cross-Platform Support: Available on desktop, mobile, and web for seamless collaboration. - Scalable Collaboration: Designed for teams of all sizes, from SMBs to large enterprises and governments. - Intuitive Interface: User-friendly design that combines speed and simplicity with enterprise security. - Open Source: Transparent development with auditable code available on GitHub. - Compliance Ready: Meets strict regulatory requirements for data protection and sovereignty. Wire offers flexible deployment options including self-hosted solutions for organizations requiring full data control. The open-source server components allow for custom deployment in private cloud or on-premises environments. Technical documentation and developer resources are available for self-hosting and integration.

Securely expose services without public IPs
Cloudflare Tunnel securely connects your origin servers, APIs, and services to Cloudflare's global network using post-quantum encrypted tunnels. Instead of exposing public IPs, you install a lightweight daemon called cloudflared on your server to create a persistent outbound-only connection. - Post-quantum encryption: Secure tunnels with advanced cryptography resistant to quantum computing threats. - No public IPs required: Eliminates the need for exposing server IP addresses to the internet. - CDN integration: Leverage Cloudflare's global CDN for caching and performance optimization. - WAF & DDoS protection: Built-in Web Application Firewall and Distributed Denial of Service mitigation. - Bot management: Advanced bot detection and mitigation to protect your services. - Granular permissions: Fine-grained access control for tunnel management. - Multi-platform support: Works with Linux, macOS, Windows, Kubernetes, and cloud providers (AWS, Azure, GCP). - Monitoring & analytics: Real-time insights into tunnel performance and traffic. - Zero Trust integration: Seamless compatibility with Cloudflare's Zero Trust security model. - Deployment: Install cloudflared daemon on your server to establish tunnels. - Configuration: Supports YAML configuration files for advanced setups. - Scalability: Designed for high availability and enterprise-grade deployments. - Open source tools: Includes Ansible, Terraform, and Kubernetes deployment guides for automation. - System requirements: Lightweight daemon with minimal resource usage (details available in system requirements).
About Zerotier
ZeroTier delivers a software-defined network overlay that connects devices, clouds, and networks anywhere in the world while improving security and reducing complexity.
Key Features of Zerotier
- Global Network Overlay: Create a virtual network that spans across the internet, connecting devices as if they were on the same local network.
- Zero Trust Security: Built-in encryption and identity-based access control ensure secure communications without complex VPN configurations.
- Cross-Platform Support: Works on Windows, macOS, Linux, Android, iOS, and embedded systems.
- Quantum-Secure Networking: ZeroTier Quantum provides end-to-end quantum-resistant encryption for future-proof security.
- Enterprise-Grade Reliability: High availability and low latency for mission-critical applications across industries like IoT, defense, finance, and healthcare.
- Developer-Friendly: RESTful API and SDKs for easy integration and automation.
- Scalability: Supports millions of devices with centralized management and monitoring.
Tech / Self-Hosting
ZeroTier operates as a managed service with optional self-hosting capabilities for the controller component. The core networking technology is open-source, allowing for custom deployments and integrations. The platform is designed for high performance and minimal overhead, making it suitable for both cloud and on-premise environments.